

- Keyspace: groups related keys.
- Key: the credential your user sends you.
- Identity: ties several keys to one user or organization.
- Root key: the credential you send to Unkey.
Keyspace
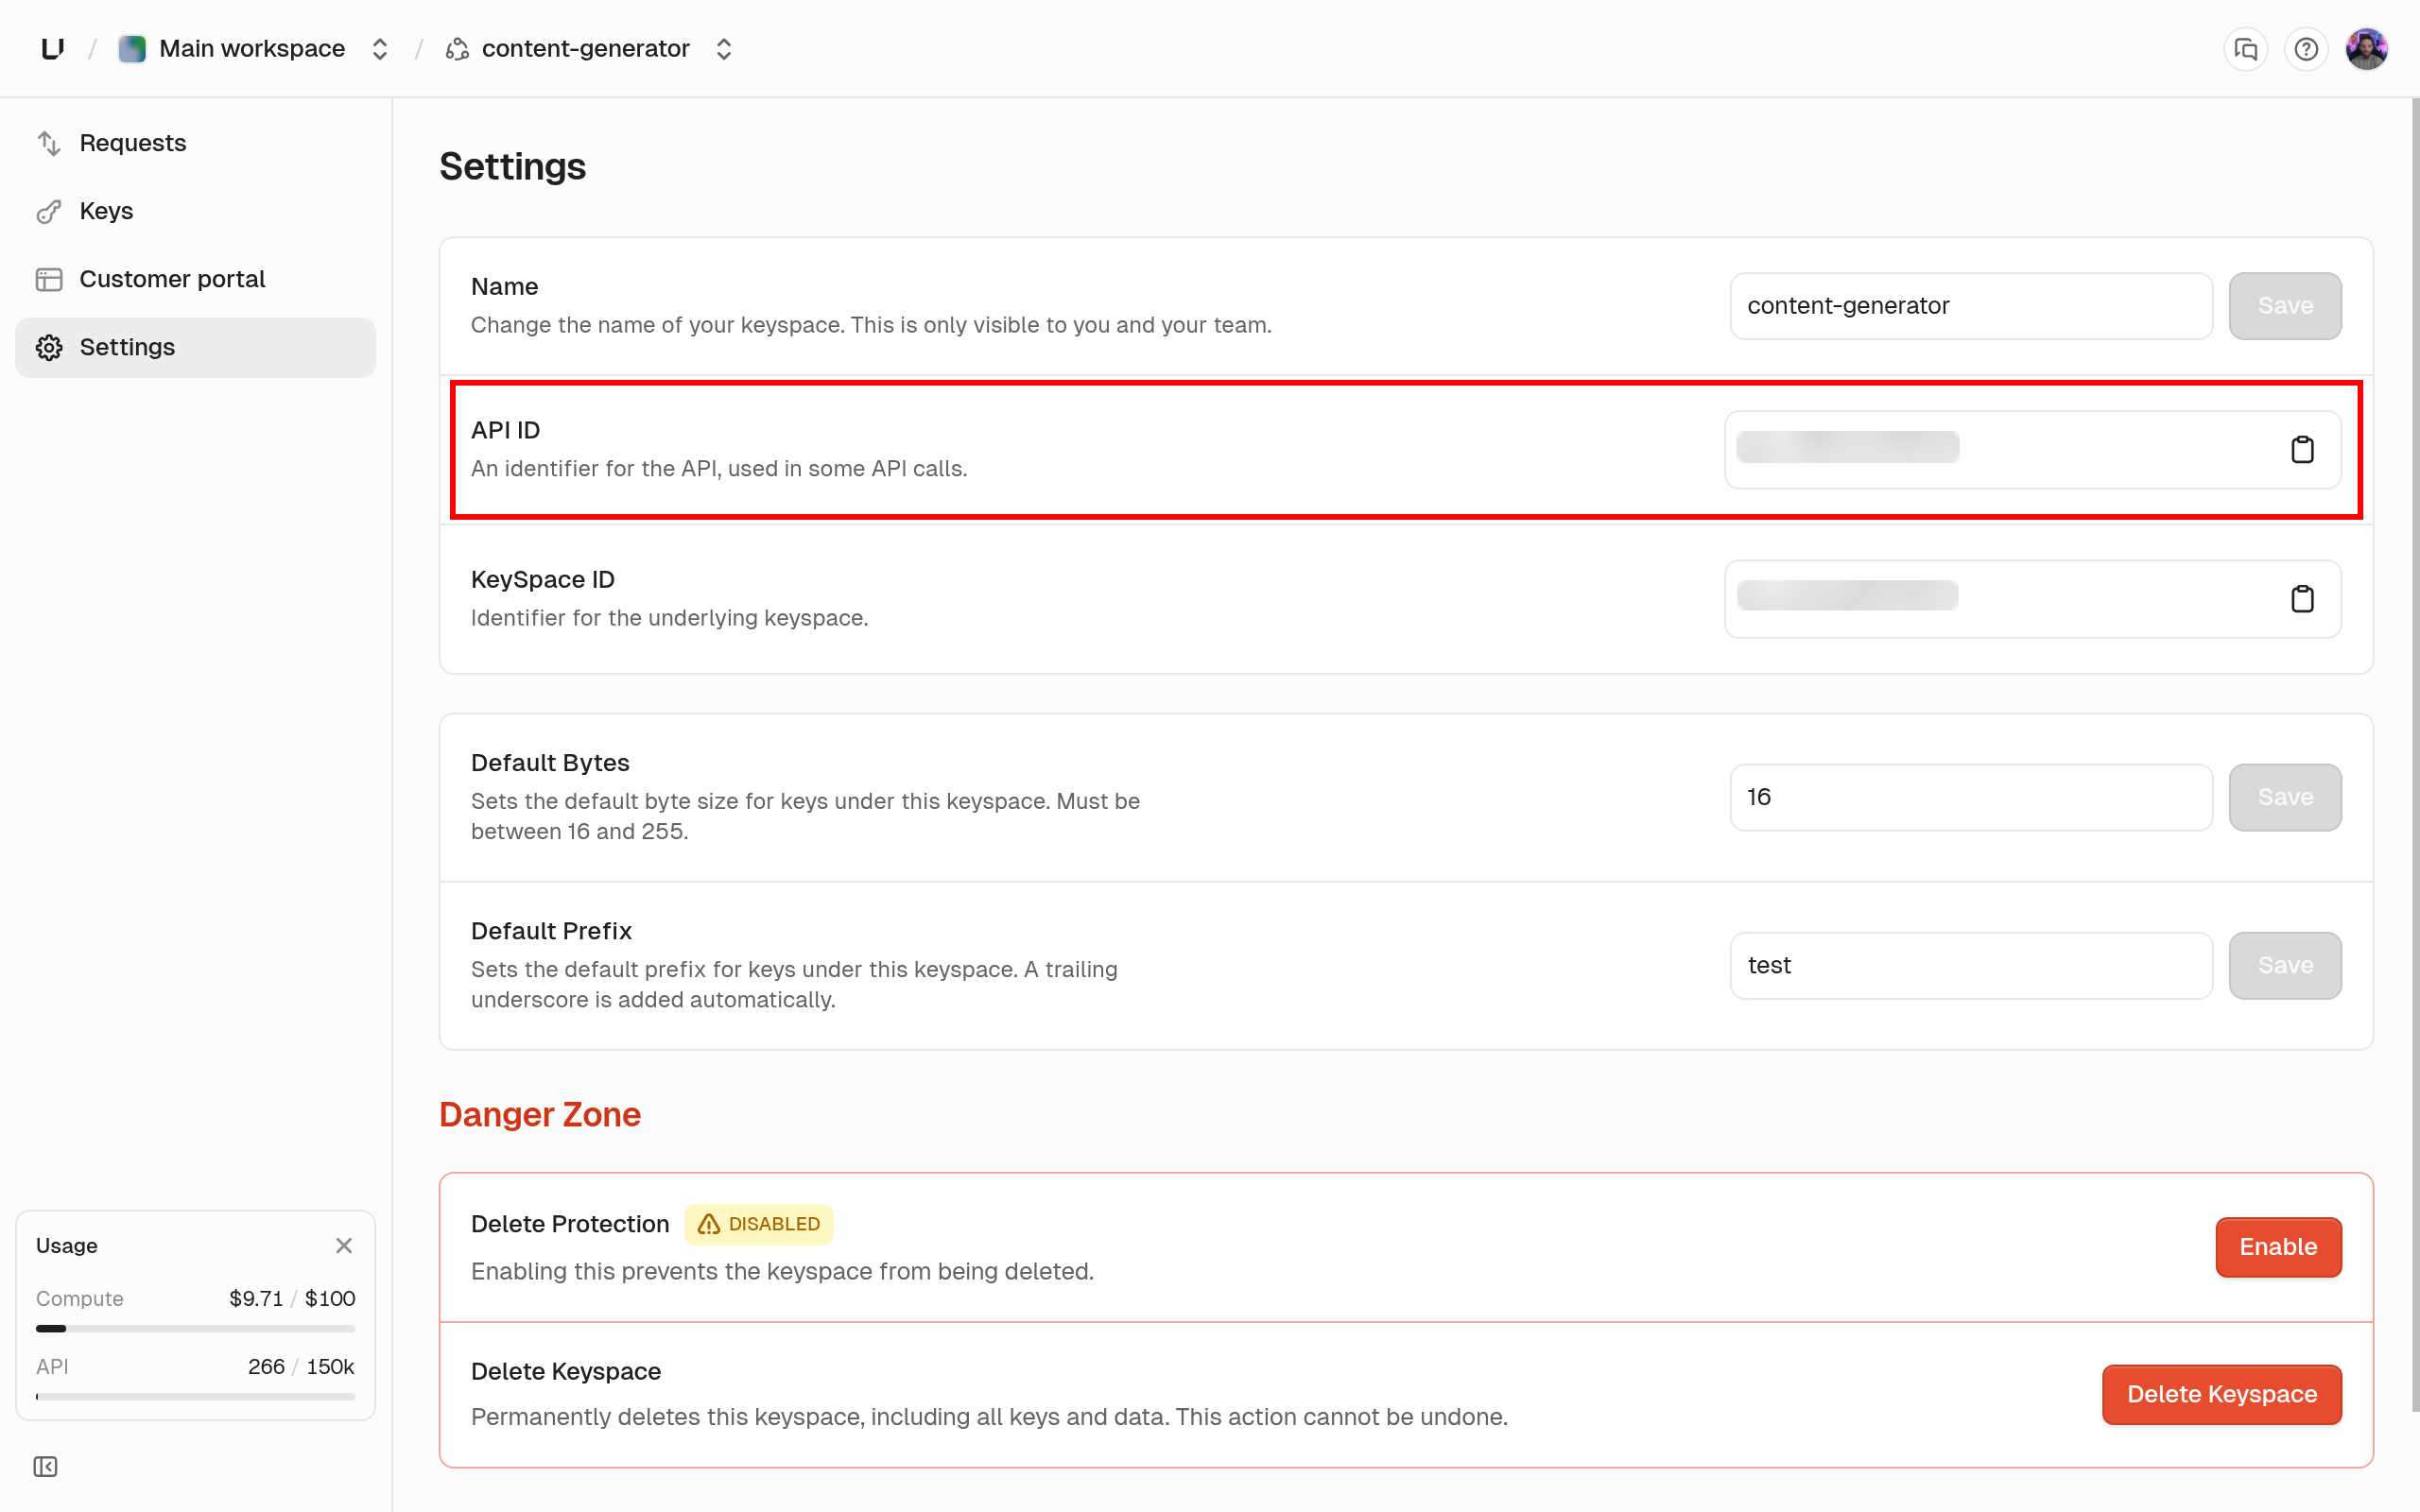
A keyspace holds related keys. You might create one per product, per such as production and staging, or per pricing tier. Every key belongs to exactly one keyspace. When you create a key, you name its keyspace by its API ID (api_...), which you’ll find on the keyspace’s settings page.
Key
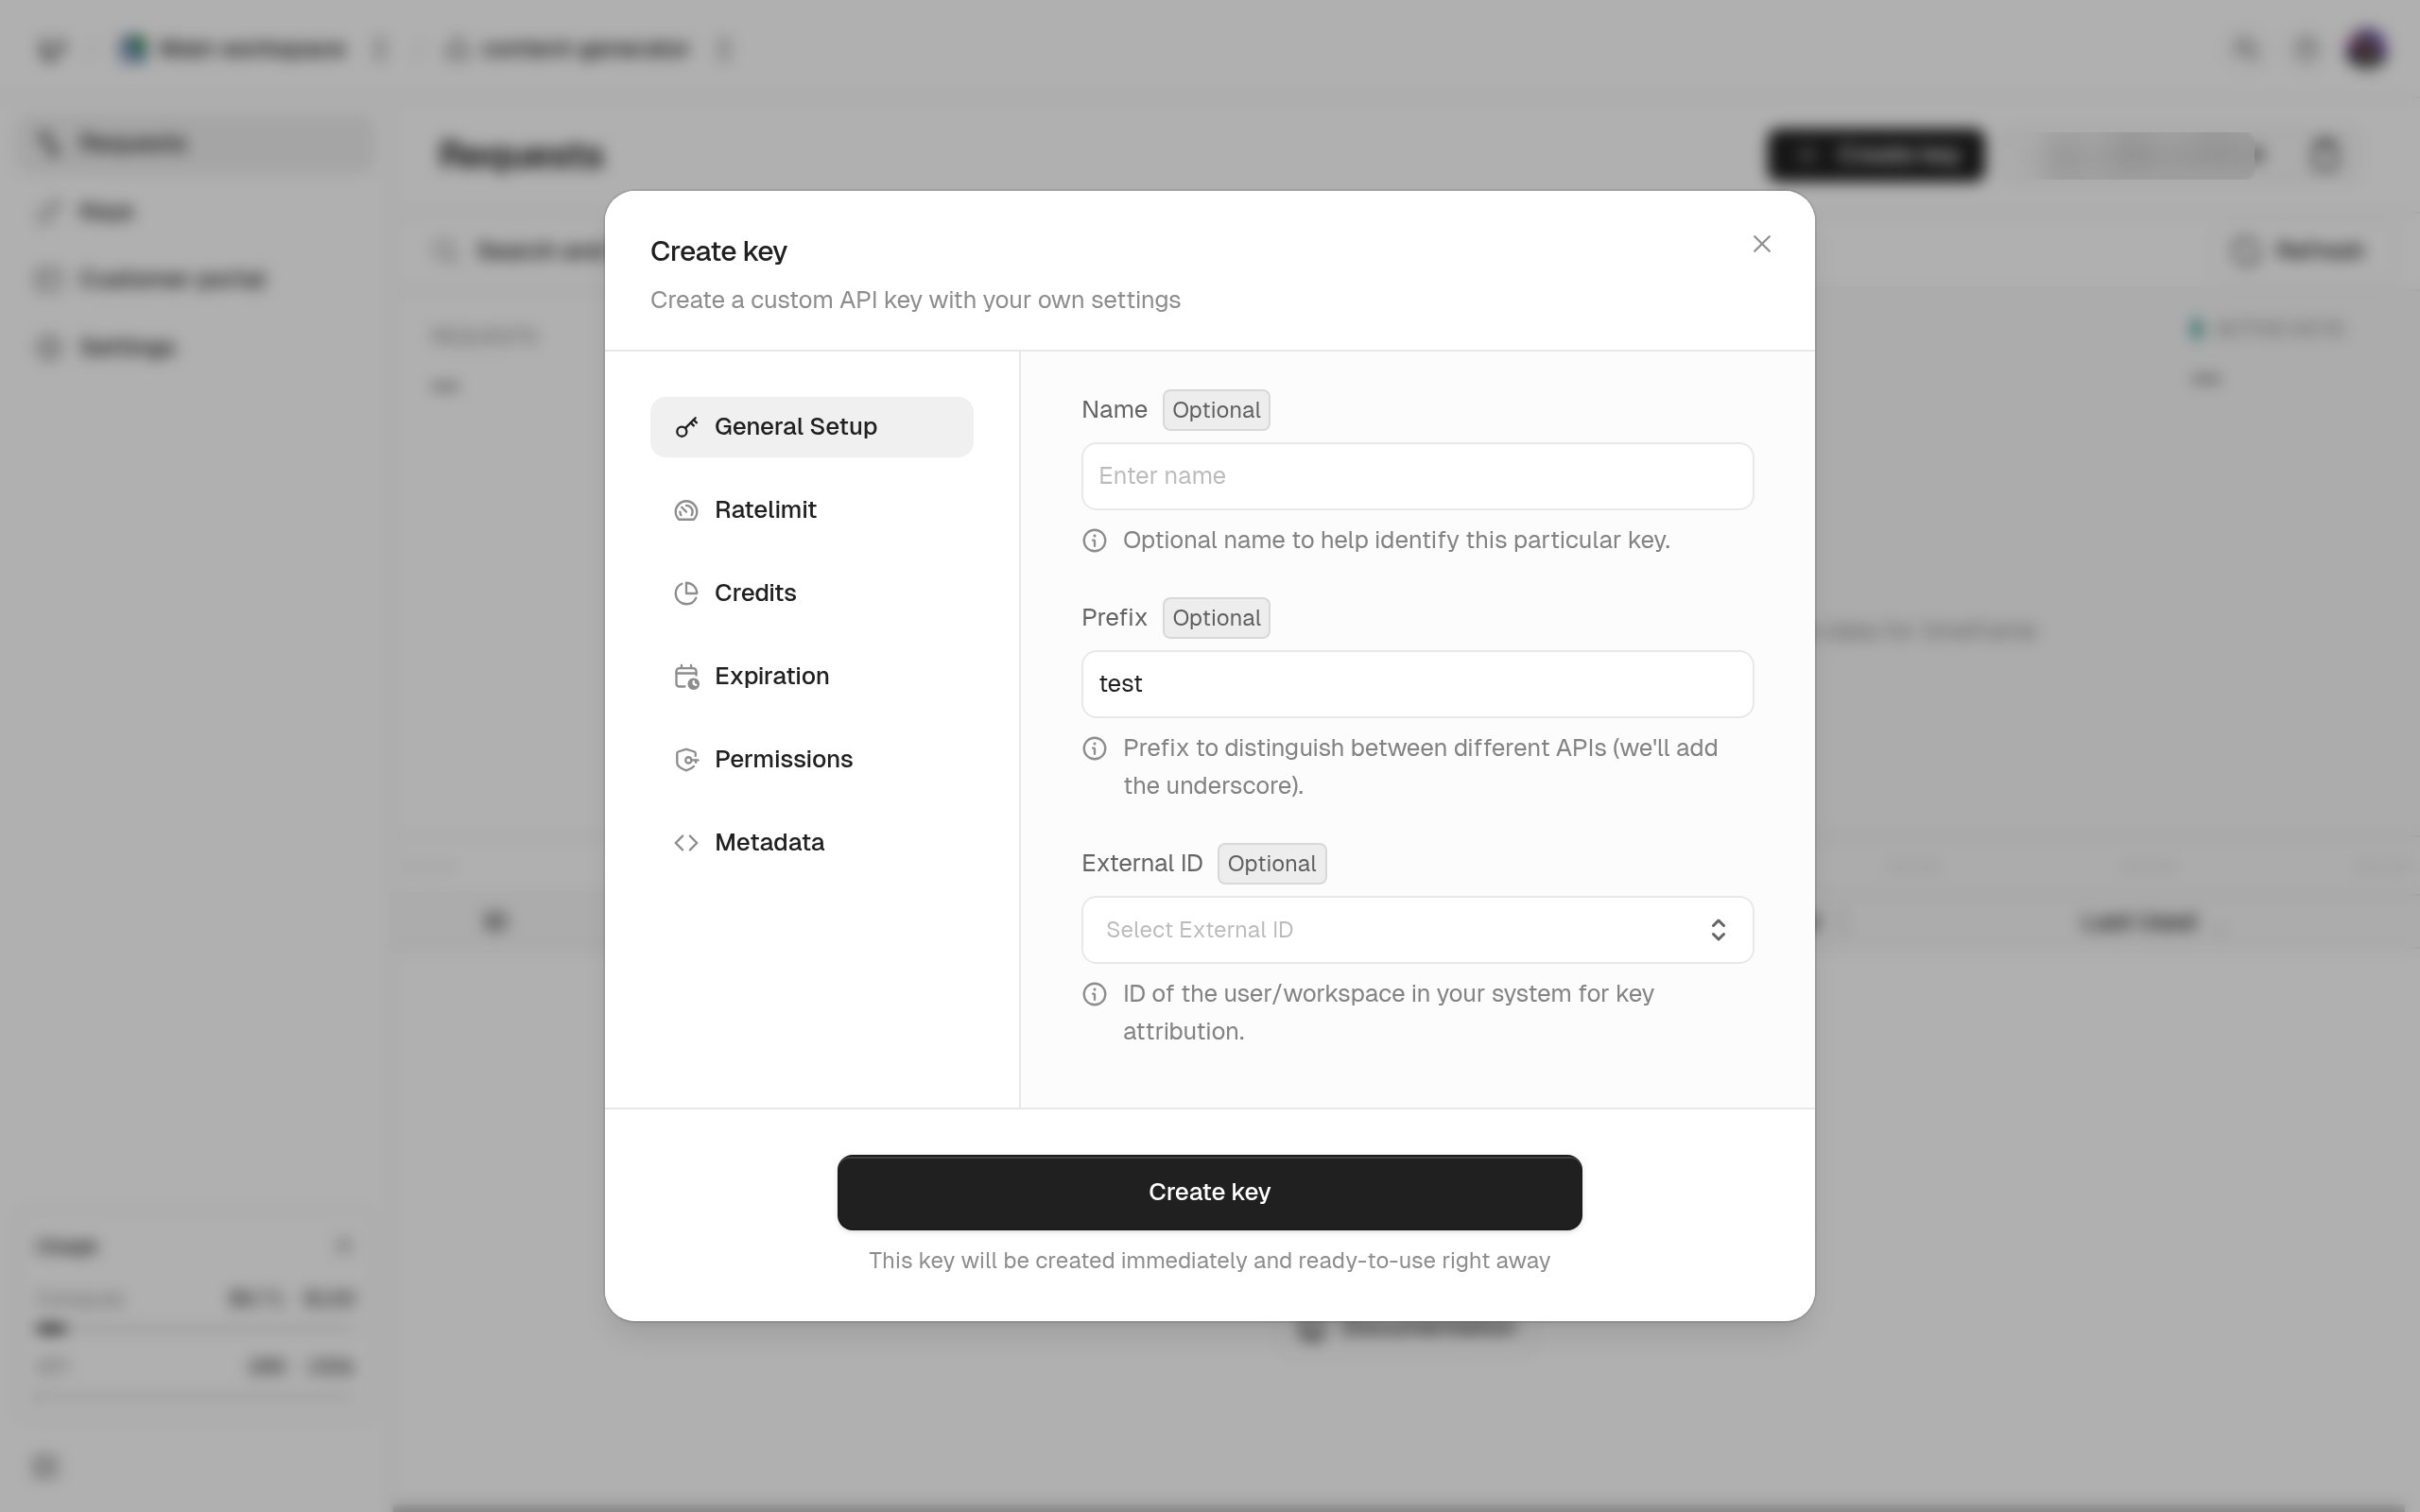
A key is a random string, with an optional prefix, that you give to your user. Unkey stores only a hash of it unless recoverable keys have been enabled. On every request, your backend sends the key tokeys.verifyKey, and Unkey runs the checks set on it.
Identity
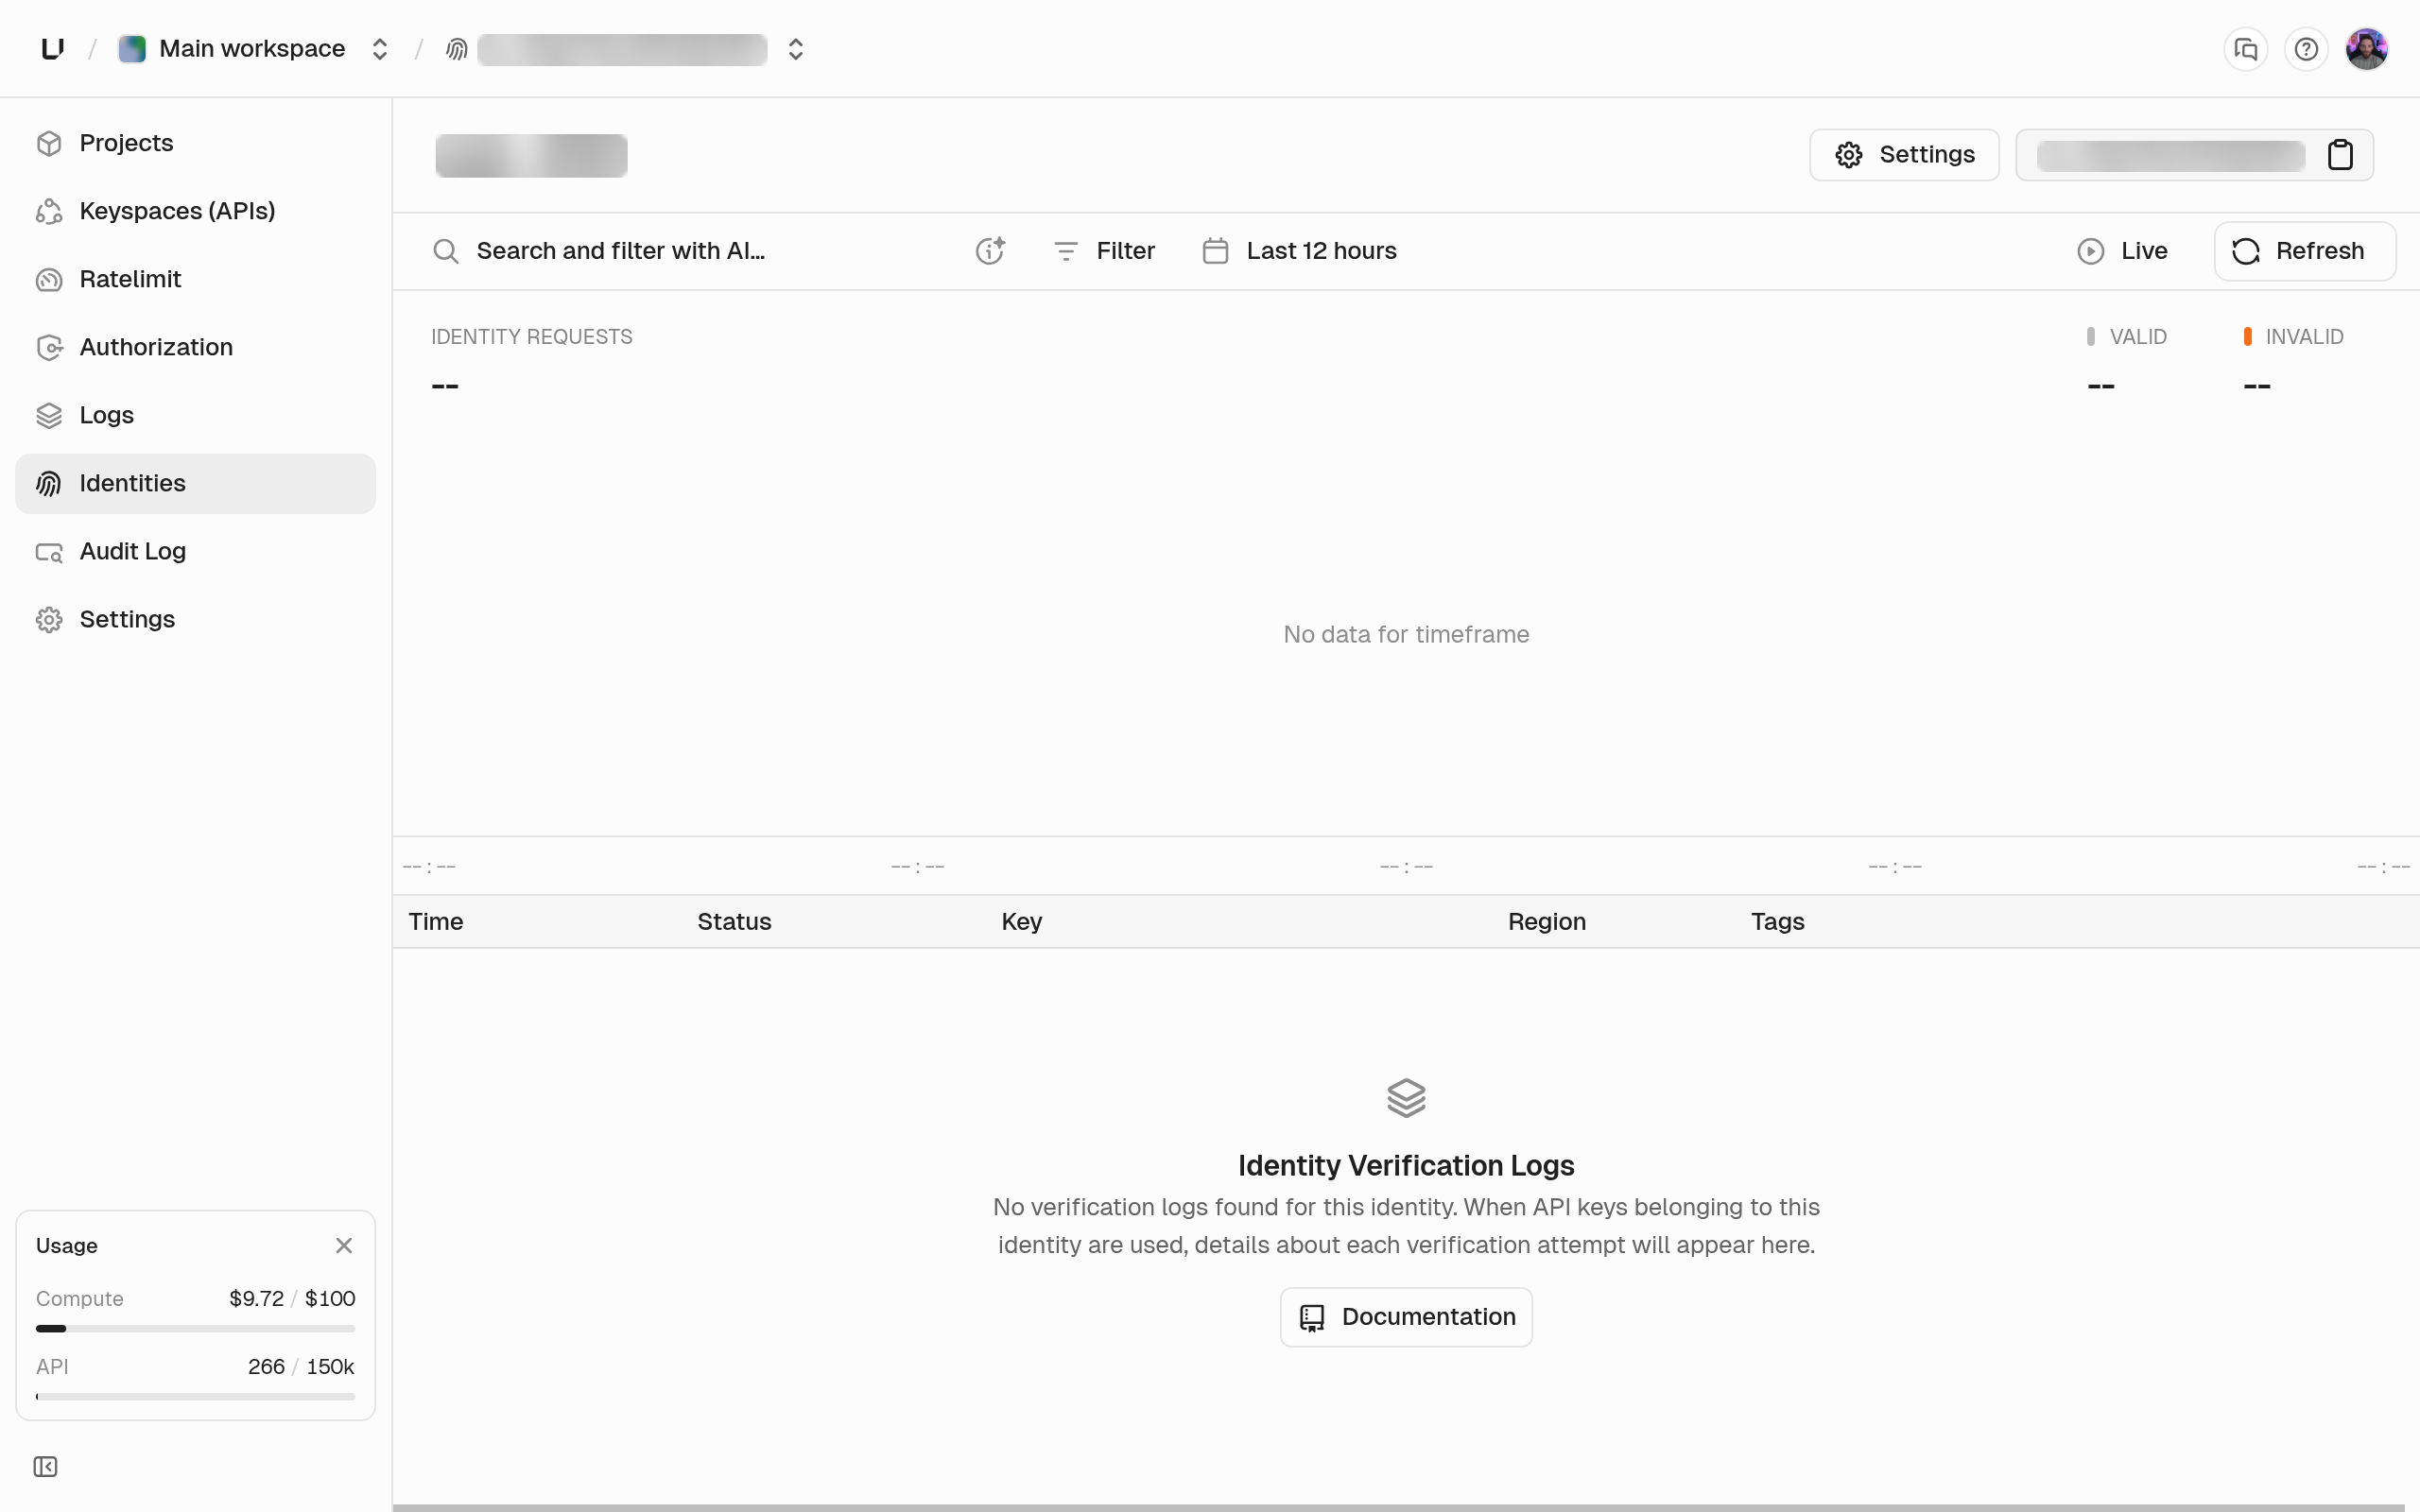
An identity represents one user, organization, or service account in your system, named by anexternalId you choose. Keys linked to the same identity share its rate limits and metadata. When you pass externalId to keys.createKey, Unkey creates the identity if it doesn’t exist and links the key to it, so most apps never call the identity endpoints directly. Identities covers this in detail.
Root key
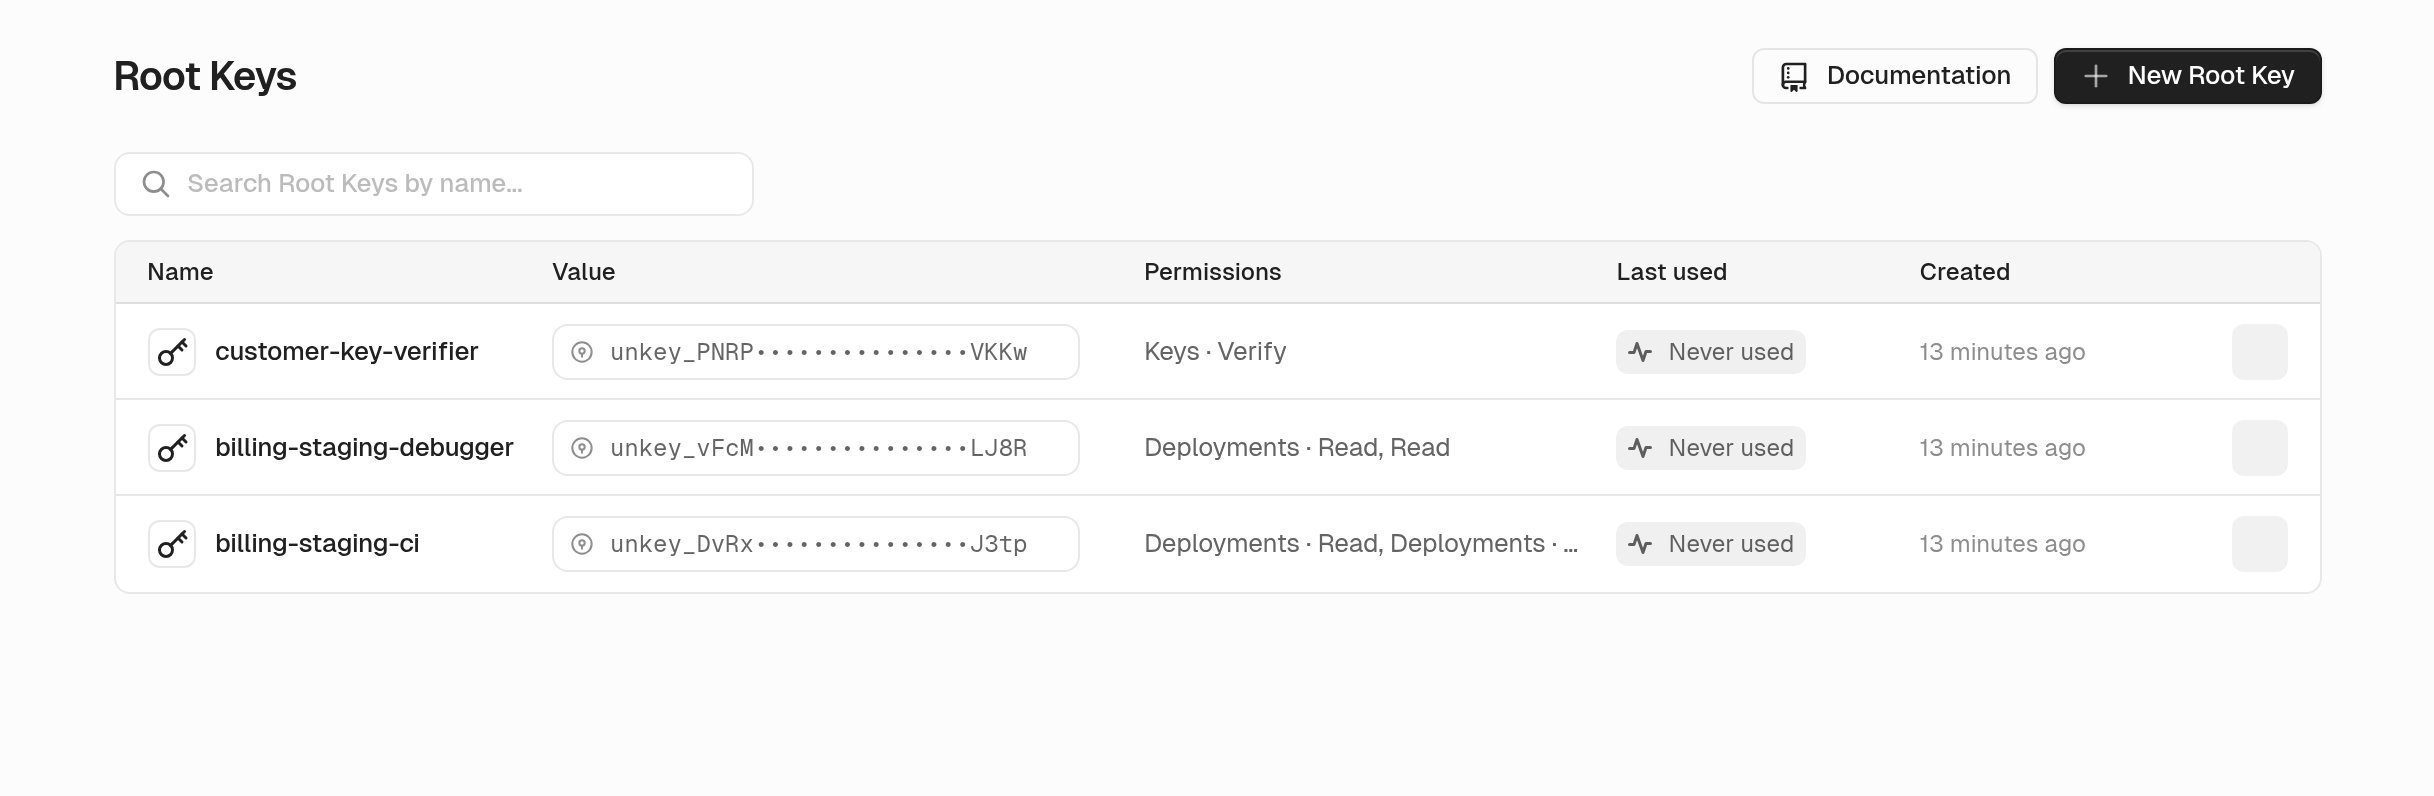
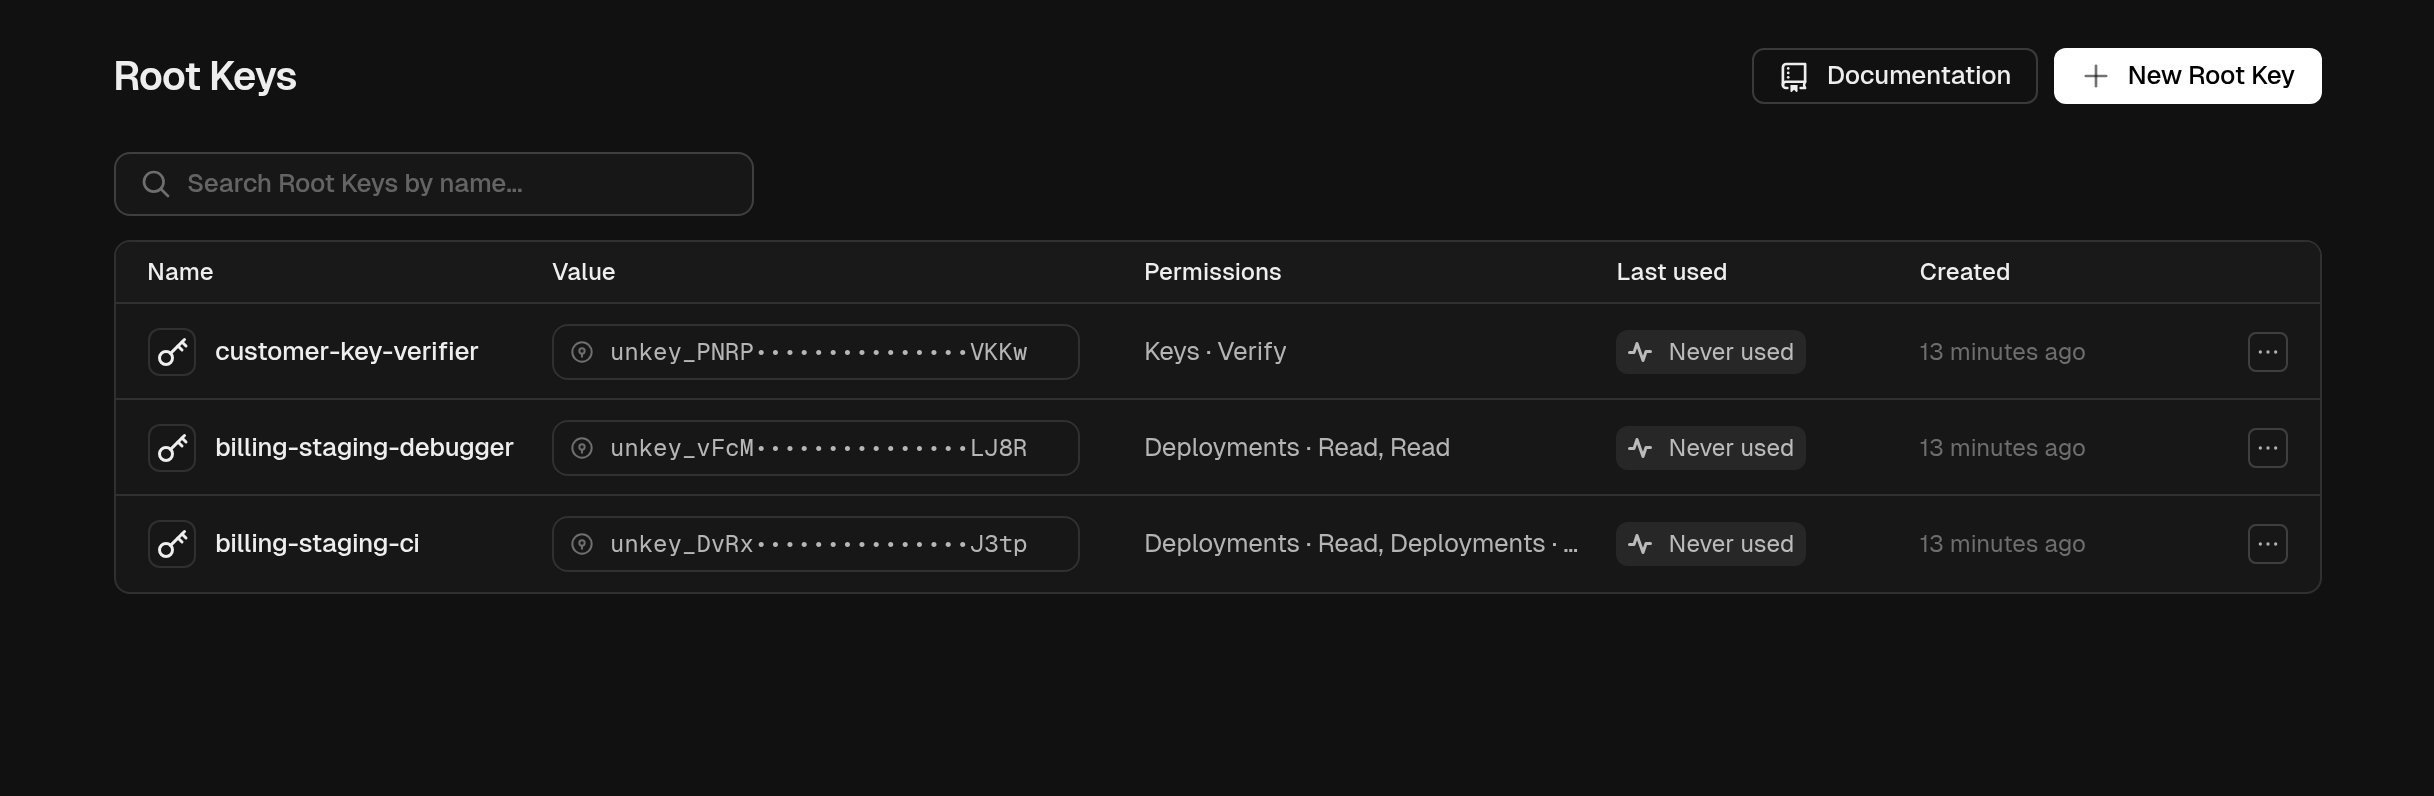
A root key authenticates you, not your users. Every call toapi.unkey.com sends a root key in the Authorization: Bearer header, and its permissions decide which calls succeed. Workspace admins create root keys from Root Keys in the dashboard sidebar. Root keys covers granting permissions and rotating keys.
How the objects relate
Next steps
Issue and verify your first key
Put the four objects to work in a few minutes.
Keyspaces
Decide how many keyspaces you need and what they store.